PexLens evaluates multiple signals together so you can make confident decisions, not guesses.
SOFTWARE SUPPLY CHAIN SECURITY
Secure software from source to production.
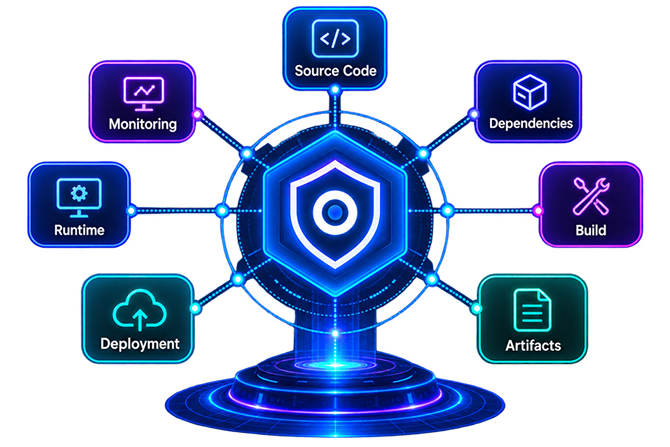
PexLens connects security signals across your software supply chain so you can reduce risk, enforce policies and ship with confidence.
End-to-end visibility across the chain
End-to-end visibility across the chain
End-to-end visibility across the chain
End-to-end visibility across the chain
Why it matters?
Risk can enter at any stage. Visibility closes the gap.
A package can have a trusted name and still introduce malicious code, known vulnerabilities, risky dependencies, or exploitable weaknesses. Even widely used packages can become compromised or introduce hidden risks that are difficult to detect through traditional security checks.
Untrusted Components
Third-party and open-source components can introduce hidden risk.
Compromised Builds
Build tools, scripts or pipelines can be tampered with.
Unknown Provenance
It's hard to trust what you can't trace back to its source.
Inconsistent Policies
Gaps in policy enforcement create blind spots.
Untrusted Components
Without complete logs, incidents are hard to investigate.
FROM REQUEST TO VERDICT
One package. Multiple security signals.
Package Information
Name, version, registry and metadata
Threat Analysis
Malicious code, suspicious behavior, indicators
Dependency Analysis
Direct & transitive dependencies
Vulnerability Analysis
Known CVEs and security weaknesses
Risk Assessment
Combined signals produce a risk score
Policy Decision
Allow, review or block
FULL VISIBILITY ACROSS THE SOFTWARE SUPPLY CHAIN
See, understand and act on risk across every stage.
From code to cloud, PexLens gives you end-to-end visibility so you can secure your entire software supply chain.
Projects Scanned
14,355
Across all devices
Total Threats
74,570
1,259,606 packages scanned
Critical + High
41,680
7,156 critical / 34,524 high
Policy Violations
312
Across all projects
Last Scan
Aug 31, 15:21
Latest scan completed
BUILT FOR MODERN TEAMS
Powerful capabilities to reduce risk and ship faster.
Policy Engine
Enforce consistent security policies at every stage.
Continuous Monitoring
Detect and respond to risks in real time.
Audit & Compliance
Complete audit trails to prove compliance with confidence.
SECURITY CONTEXT & DECISION
Understand the risks. Make the right decision.
PexLens analyzes the dependency path, evaluates security signals, and helps you enforce the right policy with confidence.
RISK SCORE
HIGH RISK
0/100
Threat level: High
What does this mean?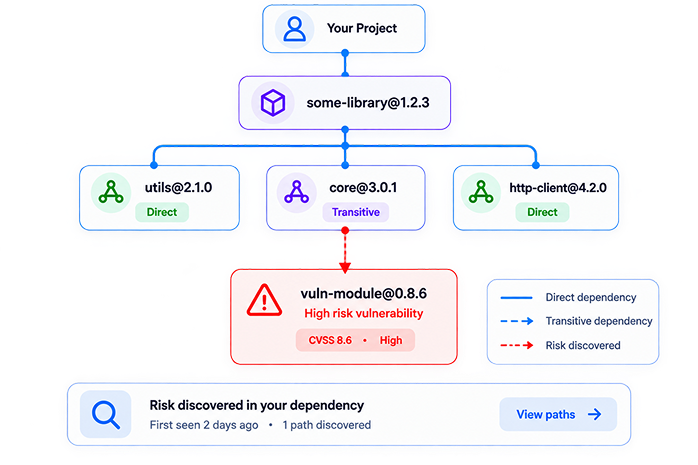
08 VISIBILITY & AUDIT TRAIL
Every decision. Every time.
Maintain complete visibility with detailed logs and audit trails for your security and compliance needs.
Scan History
View allDEVICE
LAST SCAN
THREATS
Zeenat-PC
Aug 28, 14:51
3
Build-Server-01
Aug 28, 14:16
1
Alice-MacBook
Aug 27, 16:43
0
Real-time scan visibility
Download Log
View allPACKAGE
VERSION
STATUS
lodash
4.17.21
Blocked
express
4.18.2
Allowed
ms
0.7.1
Blocked
Track all package download attempts
Audit Logs
View allEVENT
DEVICE
SEVERITY
Package blocked
Zeenat-PC
High
Policy updated
Admin
Medium
Scan completed
Zeenat-PC
Low
Comprehensive audit trail
SECURE YOUR SOFTWARE SUPPLY CHAIN
Reduce risk. Enforce policies. Ship with confidence.
PexLens helps security and engineering teams build safer software, faster.
No agent rollout required to evaluate.