Critical vulnerability
RISK ASSESSMENT
Turn complex signals into clear risk.
PexLens analyzes multiple signals across security, reputation, dependencies and behavior to deliver an explainable risk assessment for every package.
Request a DemoMulti-signal analysis
Explainable results
Actionable decisions
THE PROBLEM
Security signals are everywhere. when nothing is checking.
A package can appear legitimate while its risk is hidden across vulnerabilities, dependencies, publisher reputation, package history, and code changes. Security teams need to correlate these signals and understand their impact, not rely on a simple safe/unsafe label, to make confident decisions about whether a package can be trusted.
01
Too many signals
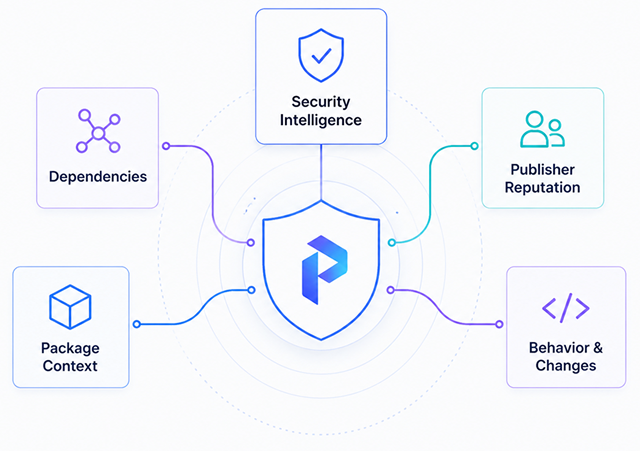
A single package can generate signals from multiple sources: vulnerabilities, dependency relationships, package metadata, publisher reputation, and behavioral or code changes.
The challenge is correlating these signals to understand their combined impact.
Vulnerabilities
Dependencies
Publisher Reputation
Package Metadata
Behaviour & Changes
02
Risk changes over time
A package that appears acceptable today may become risky after a new version, dependency change, suspicious update, or newly disclosed vulnerability.
Risk assessment must account for what has changed—not just what was known when the package was first analyzed.
03
Scores without context fail
A risk score tells you how risky a package appears, but not why. Without the underlying findings, severity, evidence, and reasoning, teams cannot confidently decide whether to install, investigate, review, or block the package.
0/100
WHY
HIGH RISK
HOW PEXLENS WORKS
One package. Multiple checks. One risk assessment.
PexLens Security Engine evaluates each package across multiple layers of security intelligence and detection logic to produce a clear, explainable risk assessment.
01
Ingest Signals
- Vulnerabilities
- Dependencies
- Publisher & metadata
- Behavior & changes
02
Correlate & Analyze
We correlate signals, analyze context, and understand what changed over time.
03
Ingest Signals
- Key findings
- Evidence
- Impact
- Recommendations
04
Ingest Signals
Make informed decisions to install, investigate, review, or block.
05
Risk Score
Continuous Assessment
Behaviour & Changes
Critical vulnerabilities detected in packages along with high correlation scores require immediate review.
Clear. Explainable. Actionable.
From raw signals to confident decisions.
Clear. Explainable. Actionable.
From raw signals to confident decisions.
EXPLAINABLE RISK
Don't just show the score.
Show why.
A risk score without context is just a number. PexLens explains what's behind the score - so you can make confident, informed security decisions.
PexLens gives reasons, not just a number
Every score is backed by clear reasons so you understand what’s driving the risk.
- Top risk factors that impact the score
- Impact level and risk contribution
- Easy to understand explanations
CVEs and vulnerabilities attached
Direct links to CVEs and vulnerability databases give you the proof you need.
- CVE ID and severity
- References to trusted sources
- Always up-to-date intelligence
Evidence you can trust and act on
Explore evidence, sources, and impact to make confident security decisions.
- Evidence from multiple sources
- Source links and advisories
- Audit-ready and shareable insights
CONTINUOUS MONITORING
Risk changes. PexLens keeps watching.
Package risk doesn't stay constant. New versions, dependency changes, and newly disclosed vulnerabilities can introduce new risk after a package has already been assessed.
PexLens continuously monitors package intelligence and reassesses risk as relevant signals change — helping security teams stay aware of changing package risk and respond when the assessment moves beyond their defined security threshold.
Version 1.0.0
Jan 10, 2024
Risk Score
0/100
LOW RISK
Initial release. Package assessed and blocked risk low.
Version 1.1.0
Feb 18, 2024
Risk Score
0/100
MEDIUM RISK
Package update. Changes in dependencies increase the risk.
New CVE Published
Mar 05, 2024
Risk Score
0/100
HIGH RISK
New vulnerability. A critical vulnerability increases the risk further.
Reassessment
Mar 05, 2024
Action
BLOCKED
Package blocked by policy.
Policy action. Risk exceeds threshold and package is blocked.
Turn signal noise into a clear answer.
Multiple security signals combined into one clear risk assessment.