DEVELOPER ENVIRONMENT SECURITY
Secure the machine
where code is written.
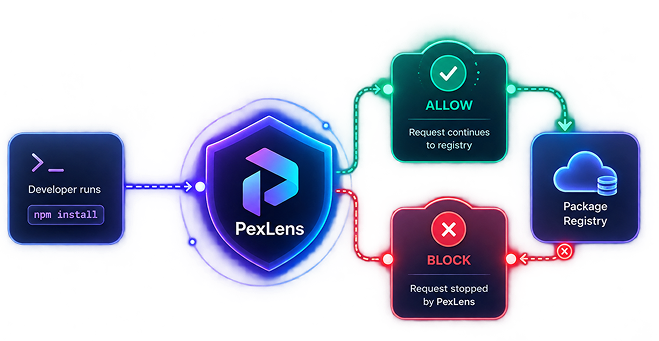
Developers install packages, dependencies and extensions dozens of times a day, on endpoints no scanner watches. PexLens checks every one of them at the moment of request — and stops the malicious ones before they execute.
Request a Demo
Four surfaces
packages, dependencies, IDE, browser
Same commands
no new developer workflow
Checked before execution
not after the install lands
THE GAP
Supply chain security stops at the pipeline.
Build systems are scanned, registries are mirrored, releases are signed. Meanwhile a developer installs an unreviewed package on a laptop with production credentials on it, and an install script runs before any of that applies.
EXECUTES FIRST
Code runs at install time
Post-install scripts execute the moment a package is fetched — long before review, CI or a scan.
HIGHEST PRIVILEGE
The richest machine in the org
Source, tokens, cloud sessions and SSH keys sit on the same endpoint that pulls untrusted code.
UNSEEN
No inventory of what landed
Most organizations cannot say which packages or extensions are on which developer machine today.
What we secure
Three ways software gets onto a developer machine
All three are covered by the same agent and the same policy — so there is no surface with a different rule.
COVERAGE
Four seconds, four checks, one verdict
Ecosystems and platforms to confirm with product before launch.
COVERAGE
Where it works today
Ecosystems and platforms to confirm with product before launch.
What security sees
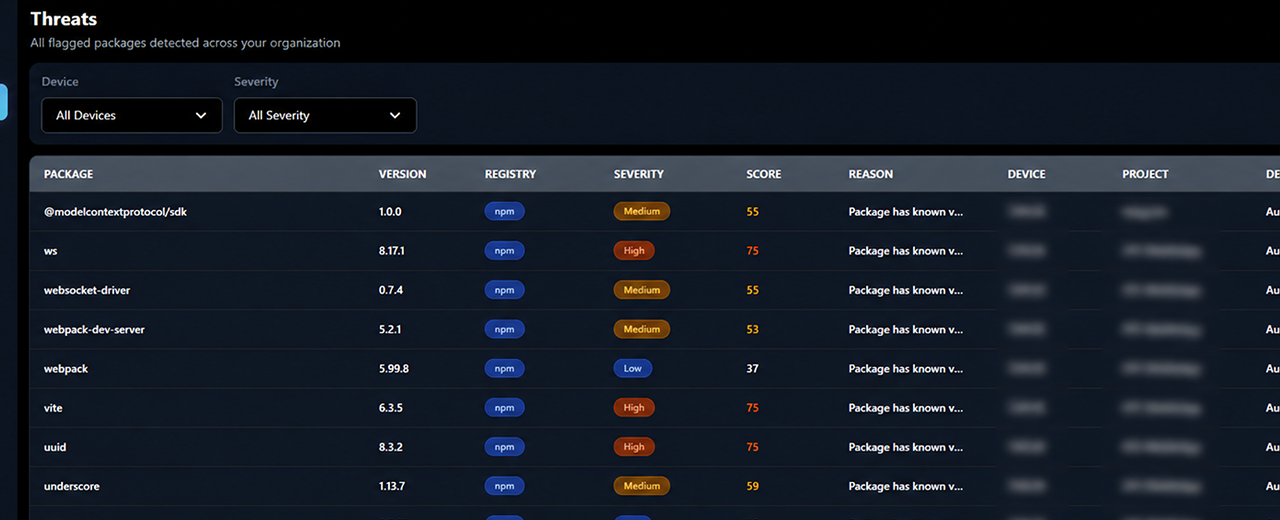
An inventory of every developer machine
Which packages and extensions are installed on which device, requested by whom, with the verdict and the reason attached — so the question "what is on our developers' laptops" finally has an answer.
Filter by device
Filter by ecosystem
Export for audit
START AT THE ENDPOINT
See what your developers installed this week.
Run PexLens on a handful of machines and we will walk you through what was requested, what would have been blocked, and why.