DEPENDENCY INTELLIGENCE
You approve one package. You ship two hundred.
PexLens resolves the full graph behind every request — direct and transitive — and carries a malicious finding upward to every package, project and machine that reaches it.
Request a Demo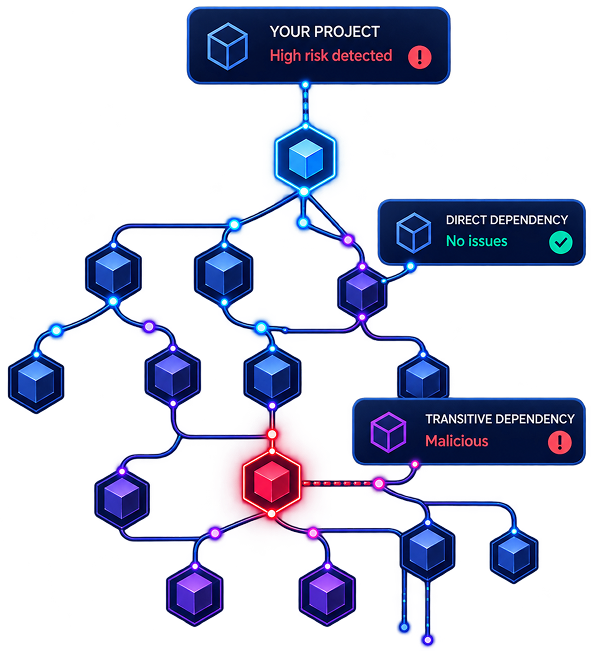
THE PROBLEM
Most of your code was chosen by somebody else.
Reviewing the package you asked for tells you little about the code that ships. The graph beneath it changes hands, versions and intent without anyone approving the change.
01
Depth hides the risk
The dangerous package is rarely in your manifest. It sits four levels down, invisible to anyone reading the dependency list.
02
One compromise spreads
When a dependency turns malicious, every package above it becomes a delivery route — across projects and machines at once.
03
The graph keeps moving
Unpinned ranges resolve differently tomorrow. A tree reviewed last month is not the tree being installed today.
WHAT PEXLENS MAPS
Six layers of dependency intelligence
A continuous supply-chain visualization mapping the risk, depth, and lineage of every package in your registry.
01
Direct dependencies
Packages your project directly depends on, including their resolved versions.
02
Transitive depth
Packages pulled in by your dependencies, revealing the full chain beneath the surface.
03
Inherited vulnerabilities
Security vulnerabilities found anywhere in the dependency tree and the packages they affect.
04
Malicious propagation
When a malicious dependency is detected, PexLens traces its path back to the packages and projects that depend on it.
05
Substitution and confusion
Identifies unexpected package resolution, substitutions, and dependencies pointing to public registries.
06
Version drift
Tracks changing dependency versions, unpinned ranges, and packages that resolve differently over time.
THE GRAPH UNDER WATCH
The tree you approved is not the tree you install
Graphs are re-resolved as versions publish, and every parent is reassessed when a child changes.
DAY 0 · L0
Graph resolved
241 packages mapped across four levels, no findings.
0/100
DAY 14 · L2
New child added
A minor release pulls in two dependencies nobody reviewed.
0/100
DAY 15 · L4
Child turns malicious
Obfuscated exfiltration logic found four levels down.
0/100
DAY 15 · L4
Child turns malicious
Obfuscated exfiltration logic found four levels down.
BLOCKED
See what's hiding in your dependency tree.
Trace every direct and transitive dependency back to its real risk.